
HTTPS and certificate
Valid certificate, auto-renewal confirmed, and every plain HTTP request redirected before any content is served.
Before a site goes live, we run it through the same checks an attacker's automated tools would run — then fix what we find and write it down in plain English. Here's the actual report you get.
A real example, written for a fictional client. Same format you'd receive — what was checked, what was fixed, and what is honestly outside our reach.
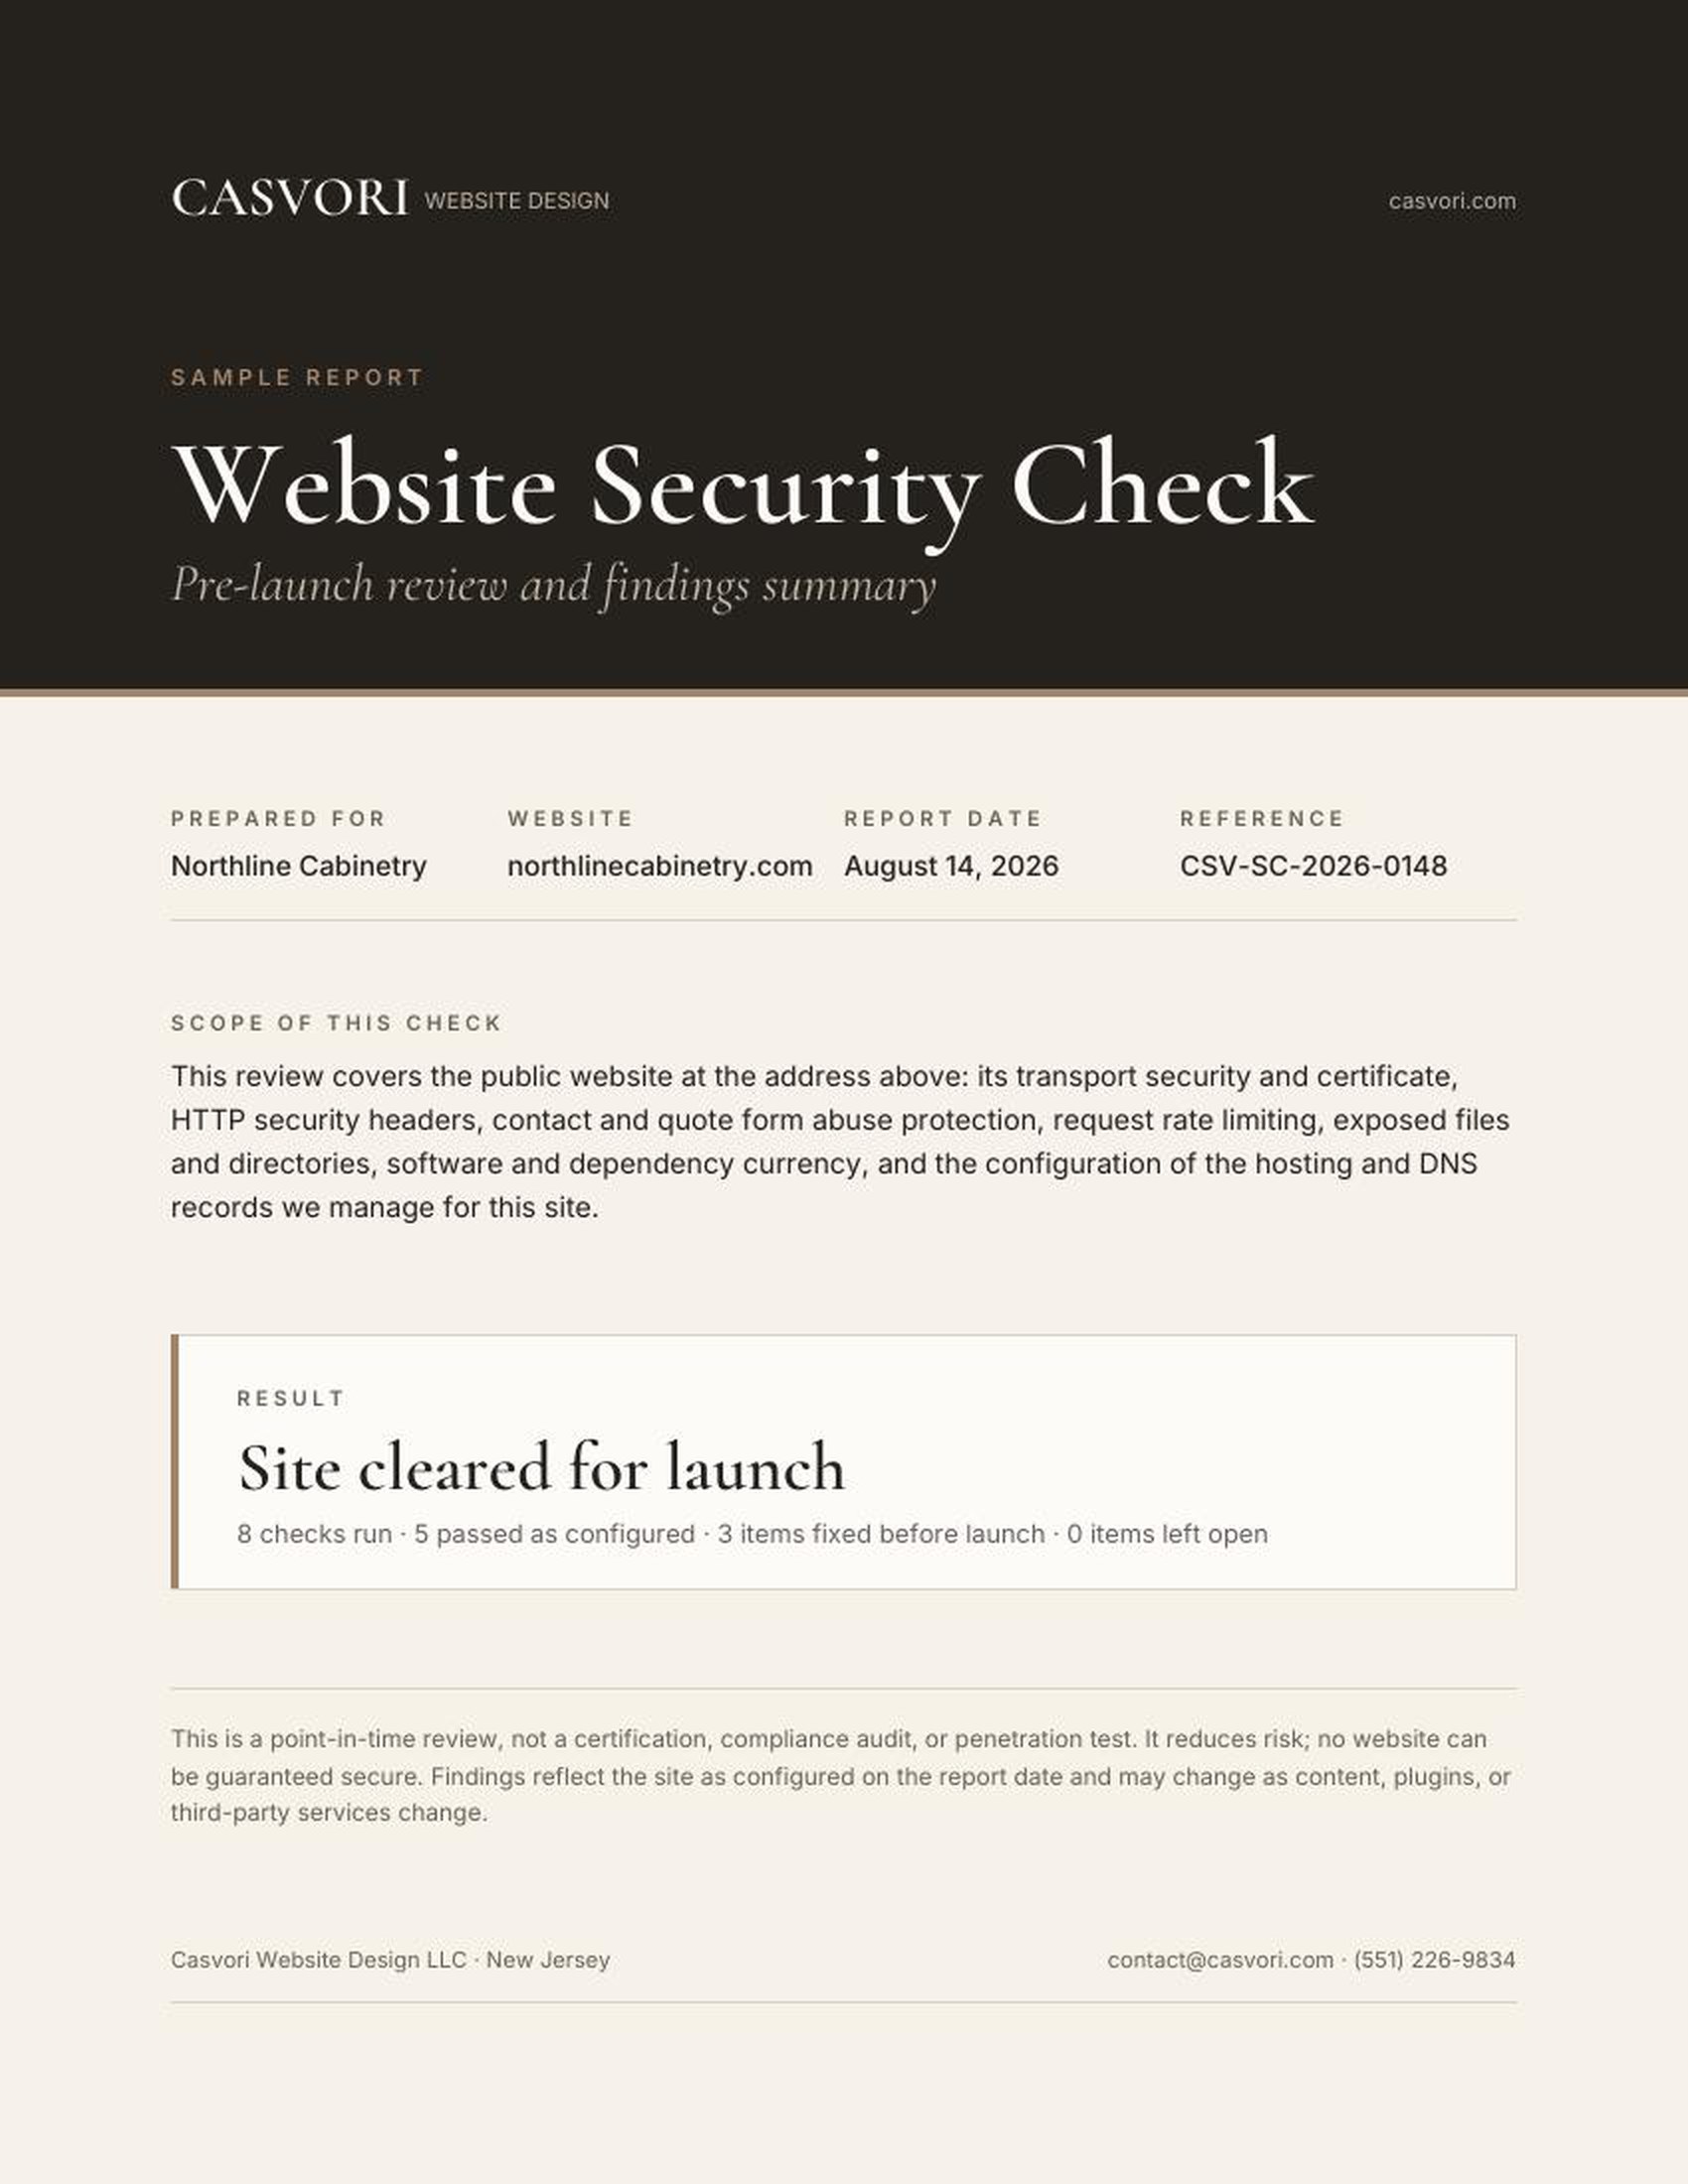
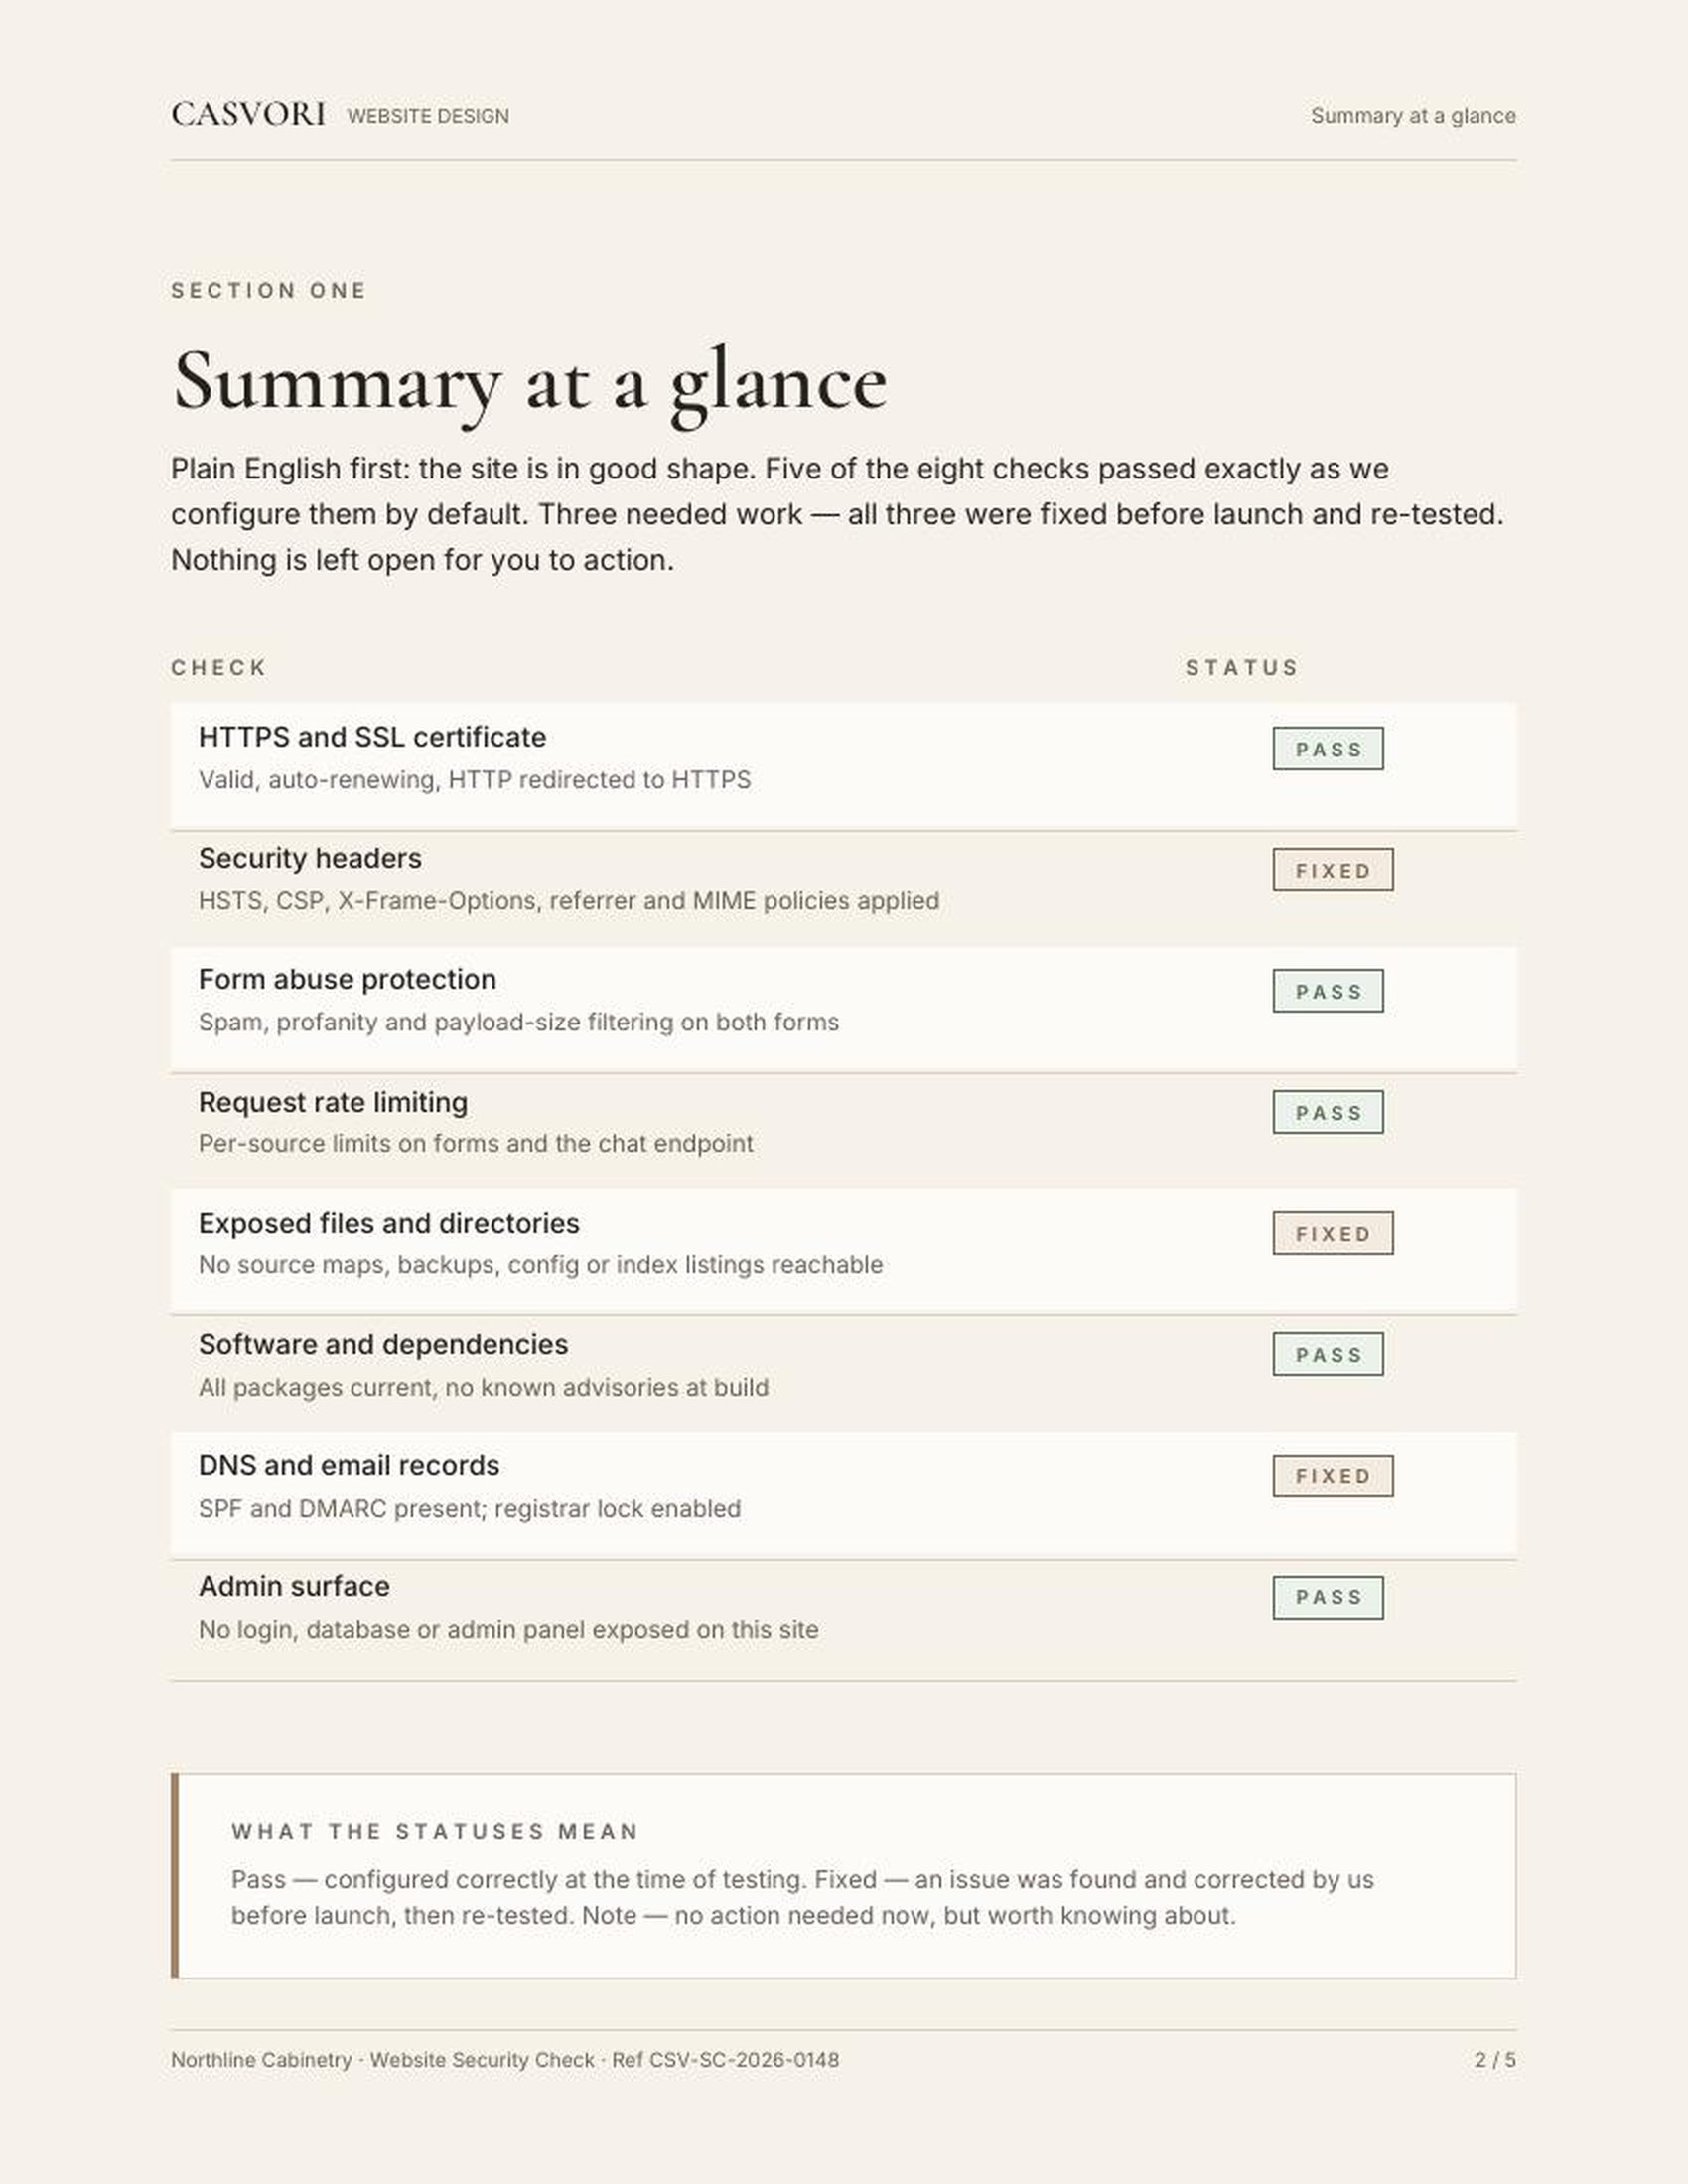
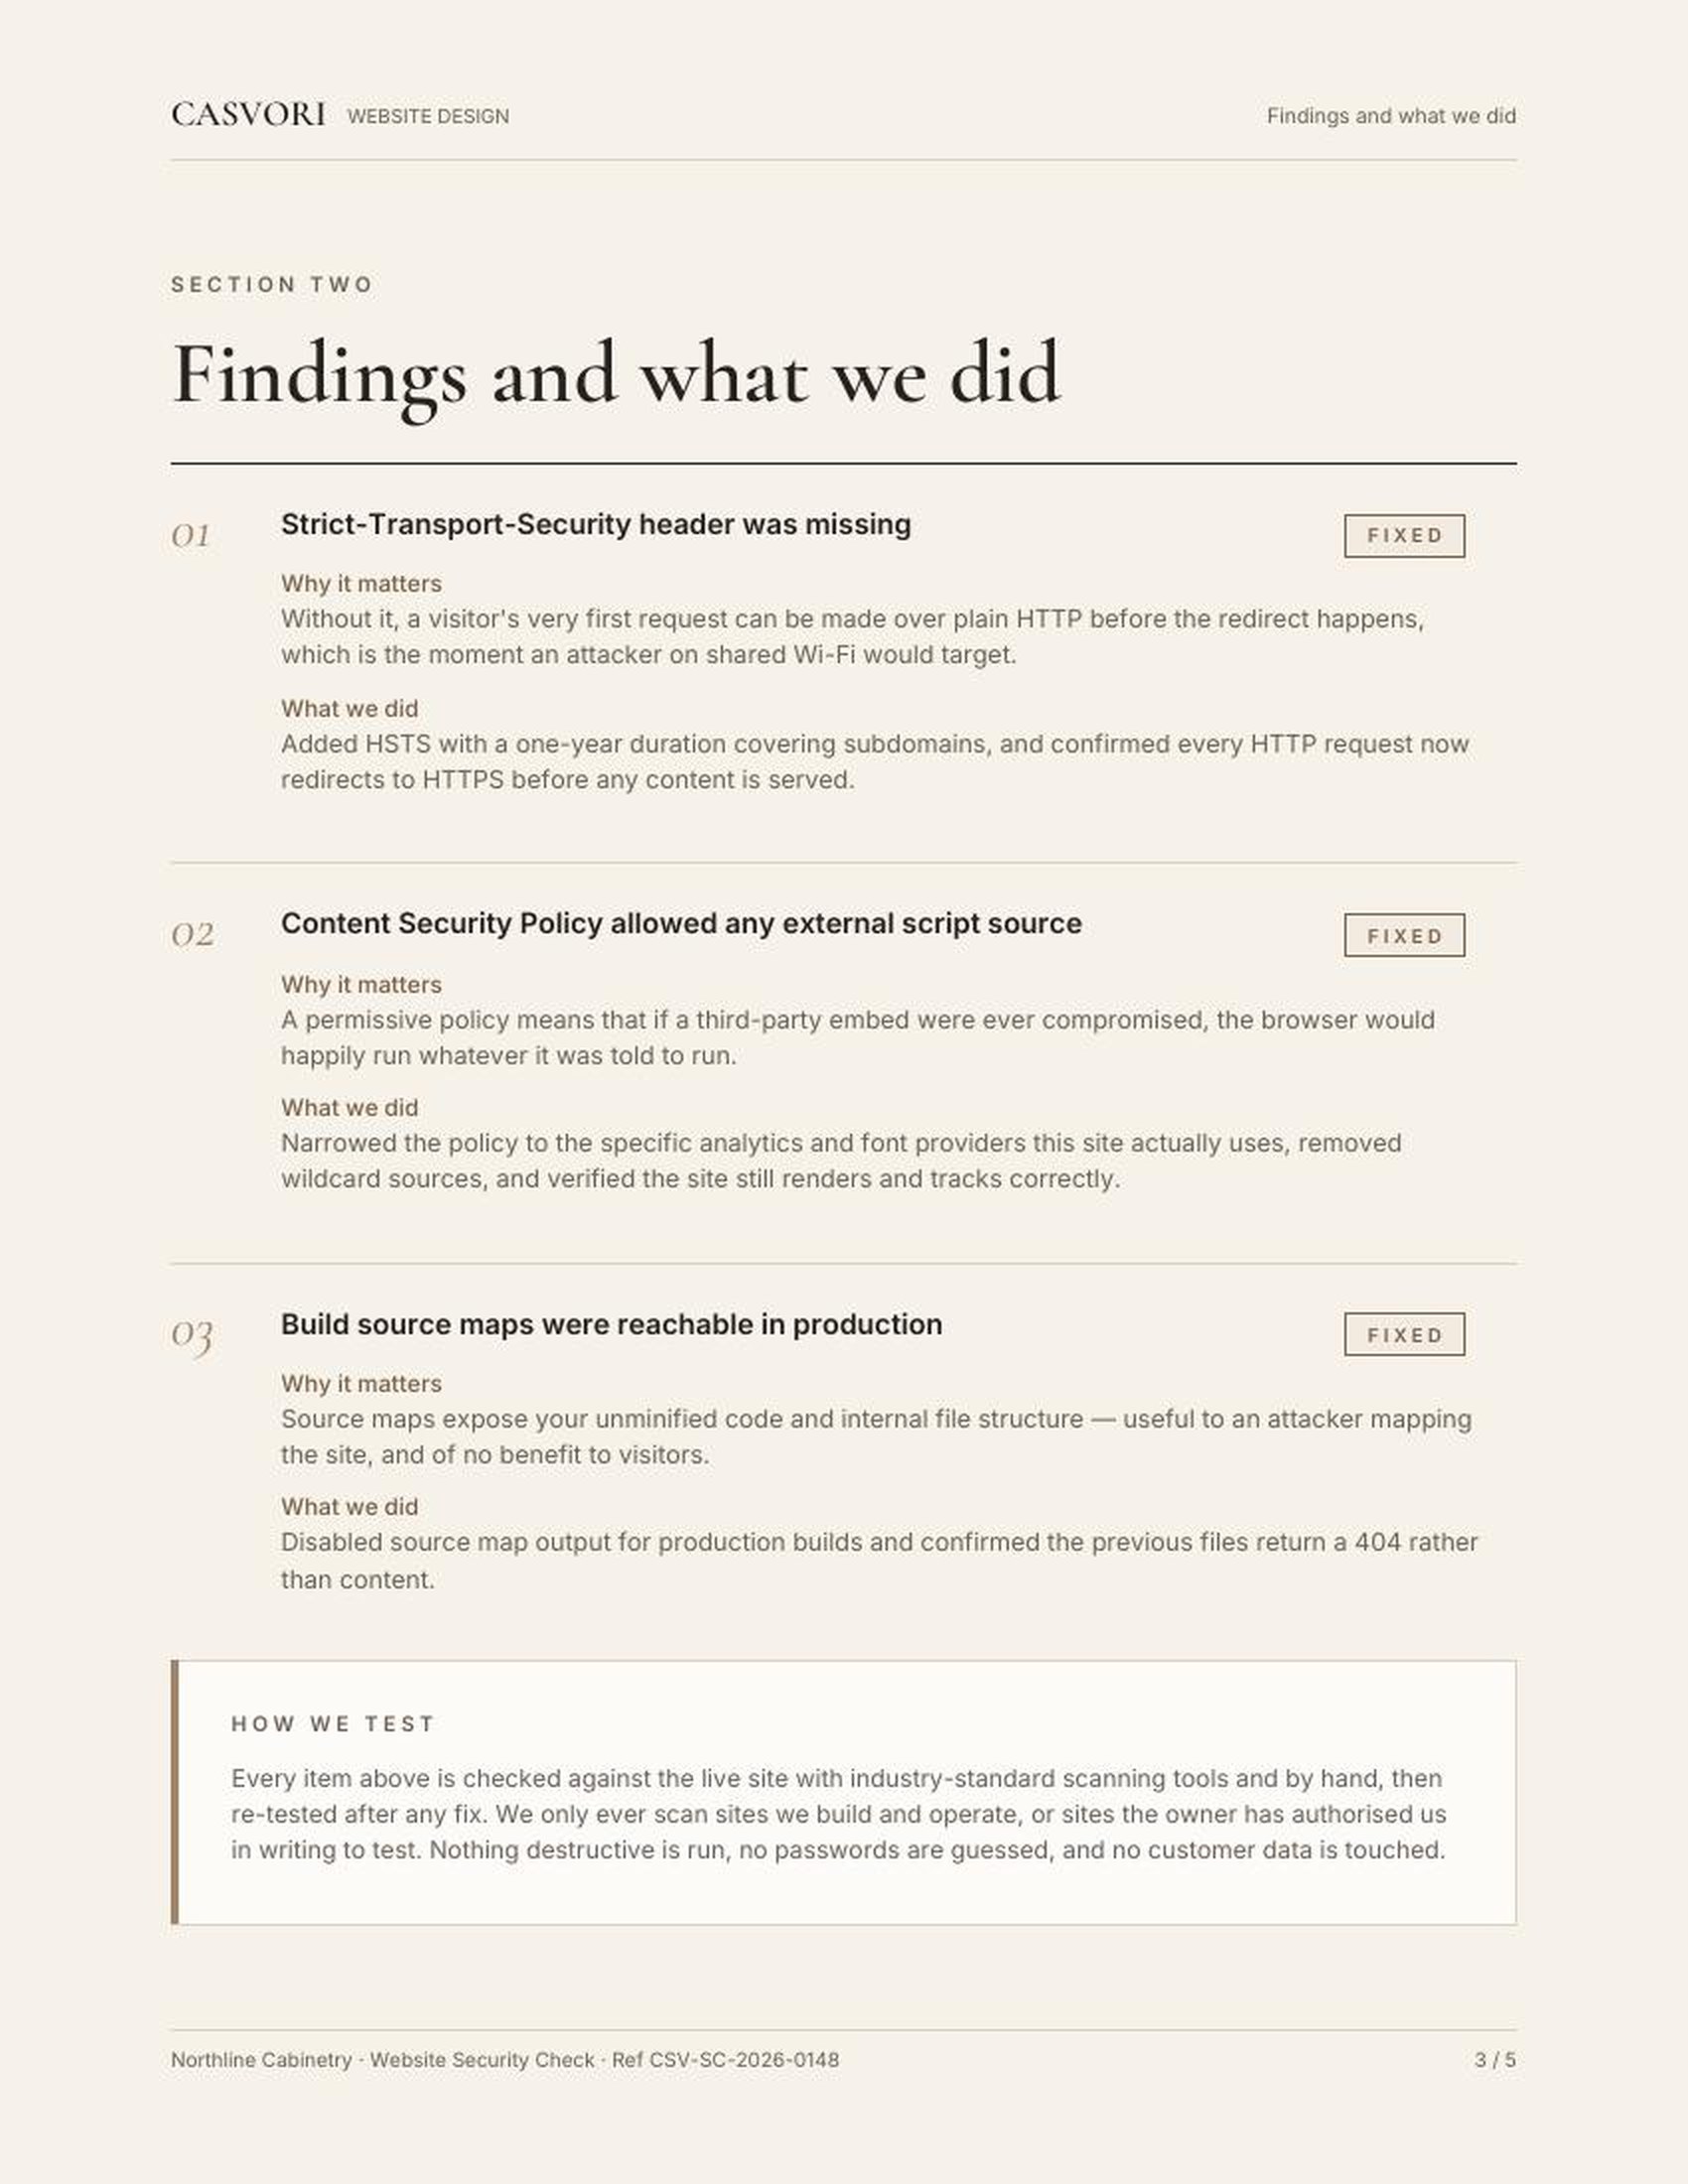
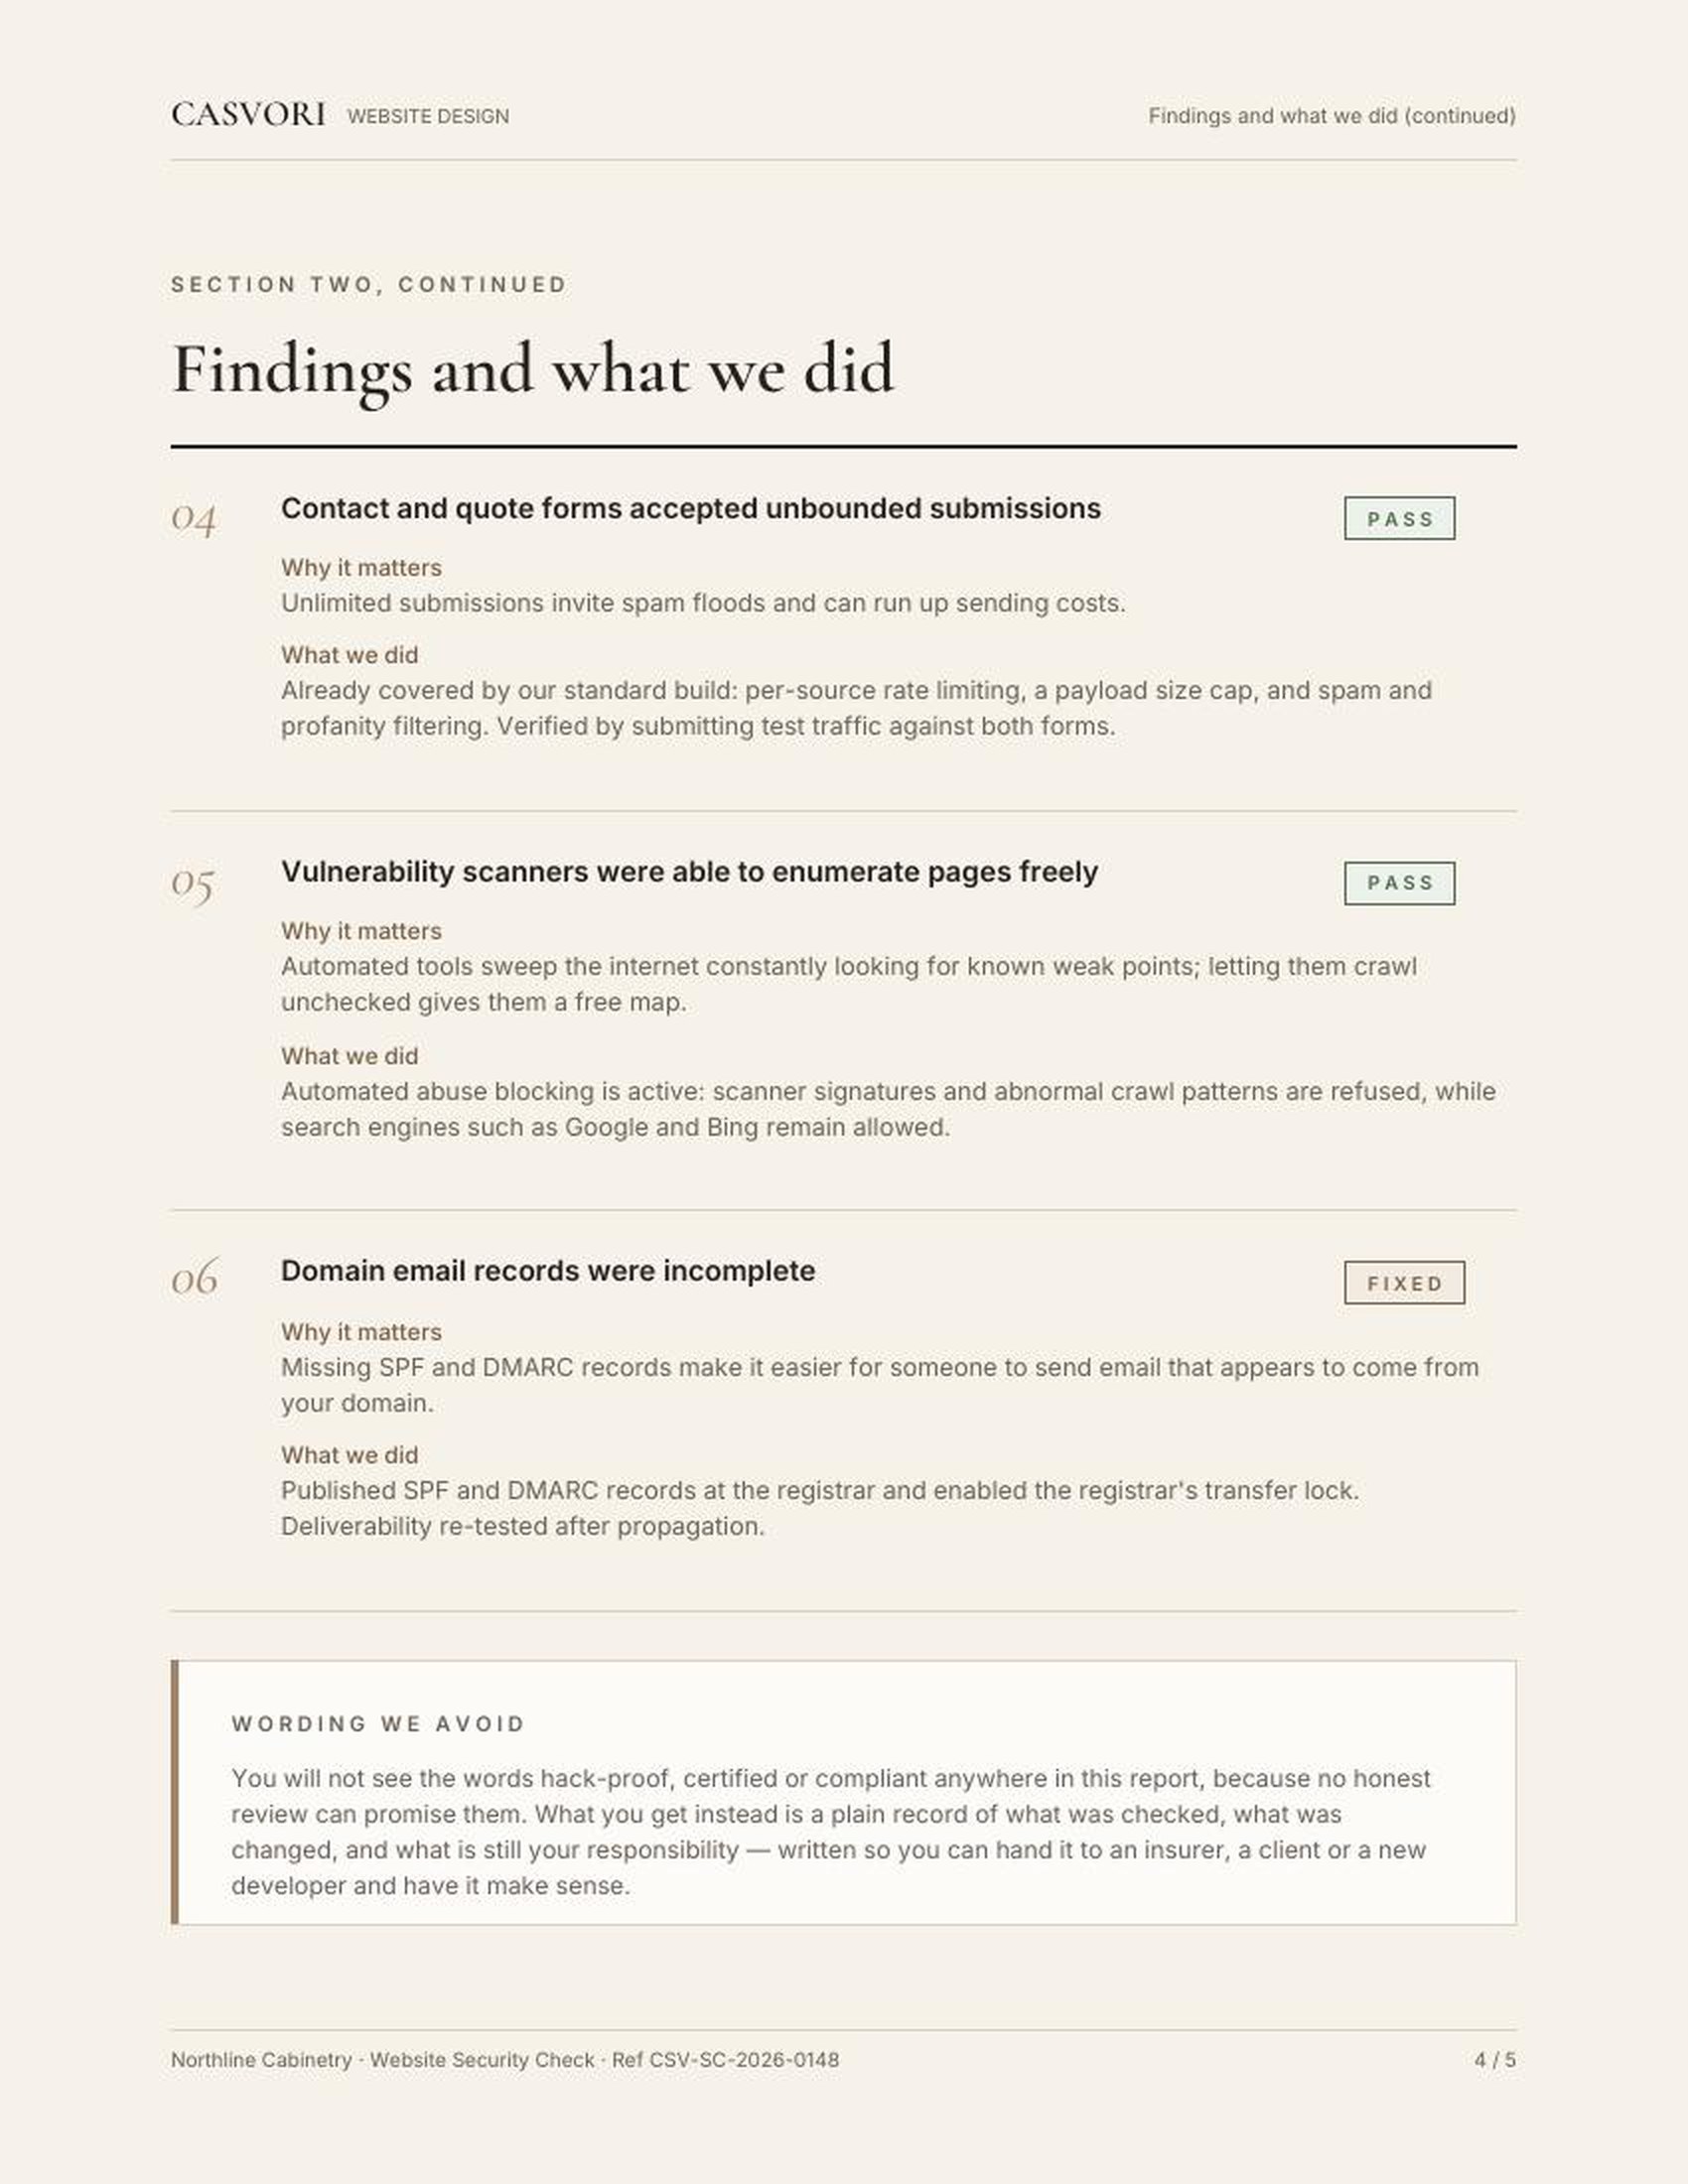
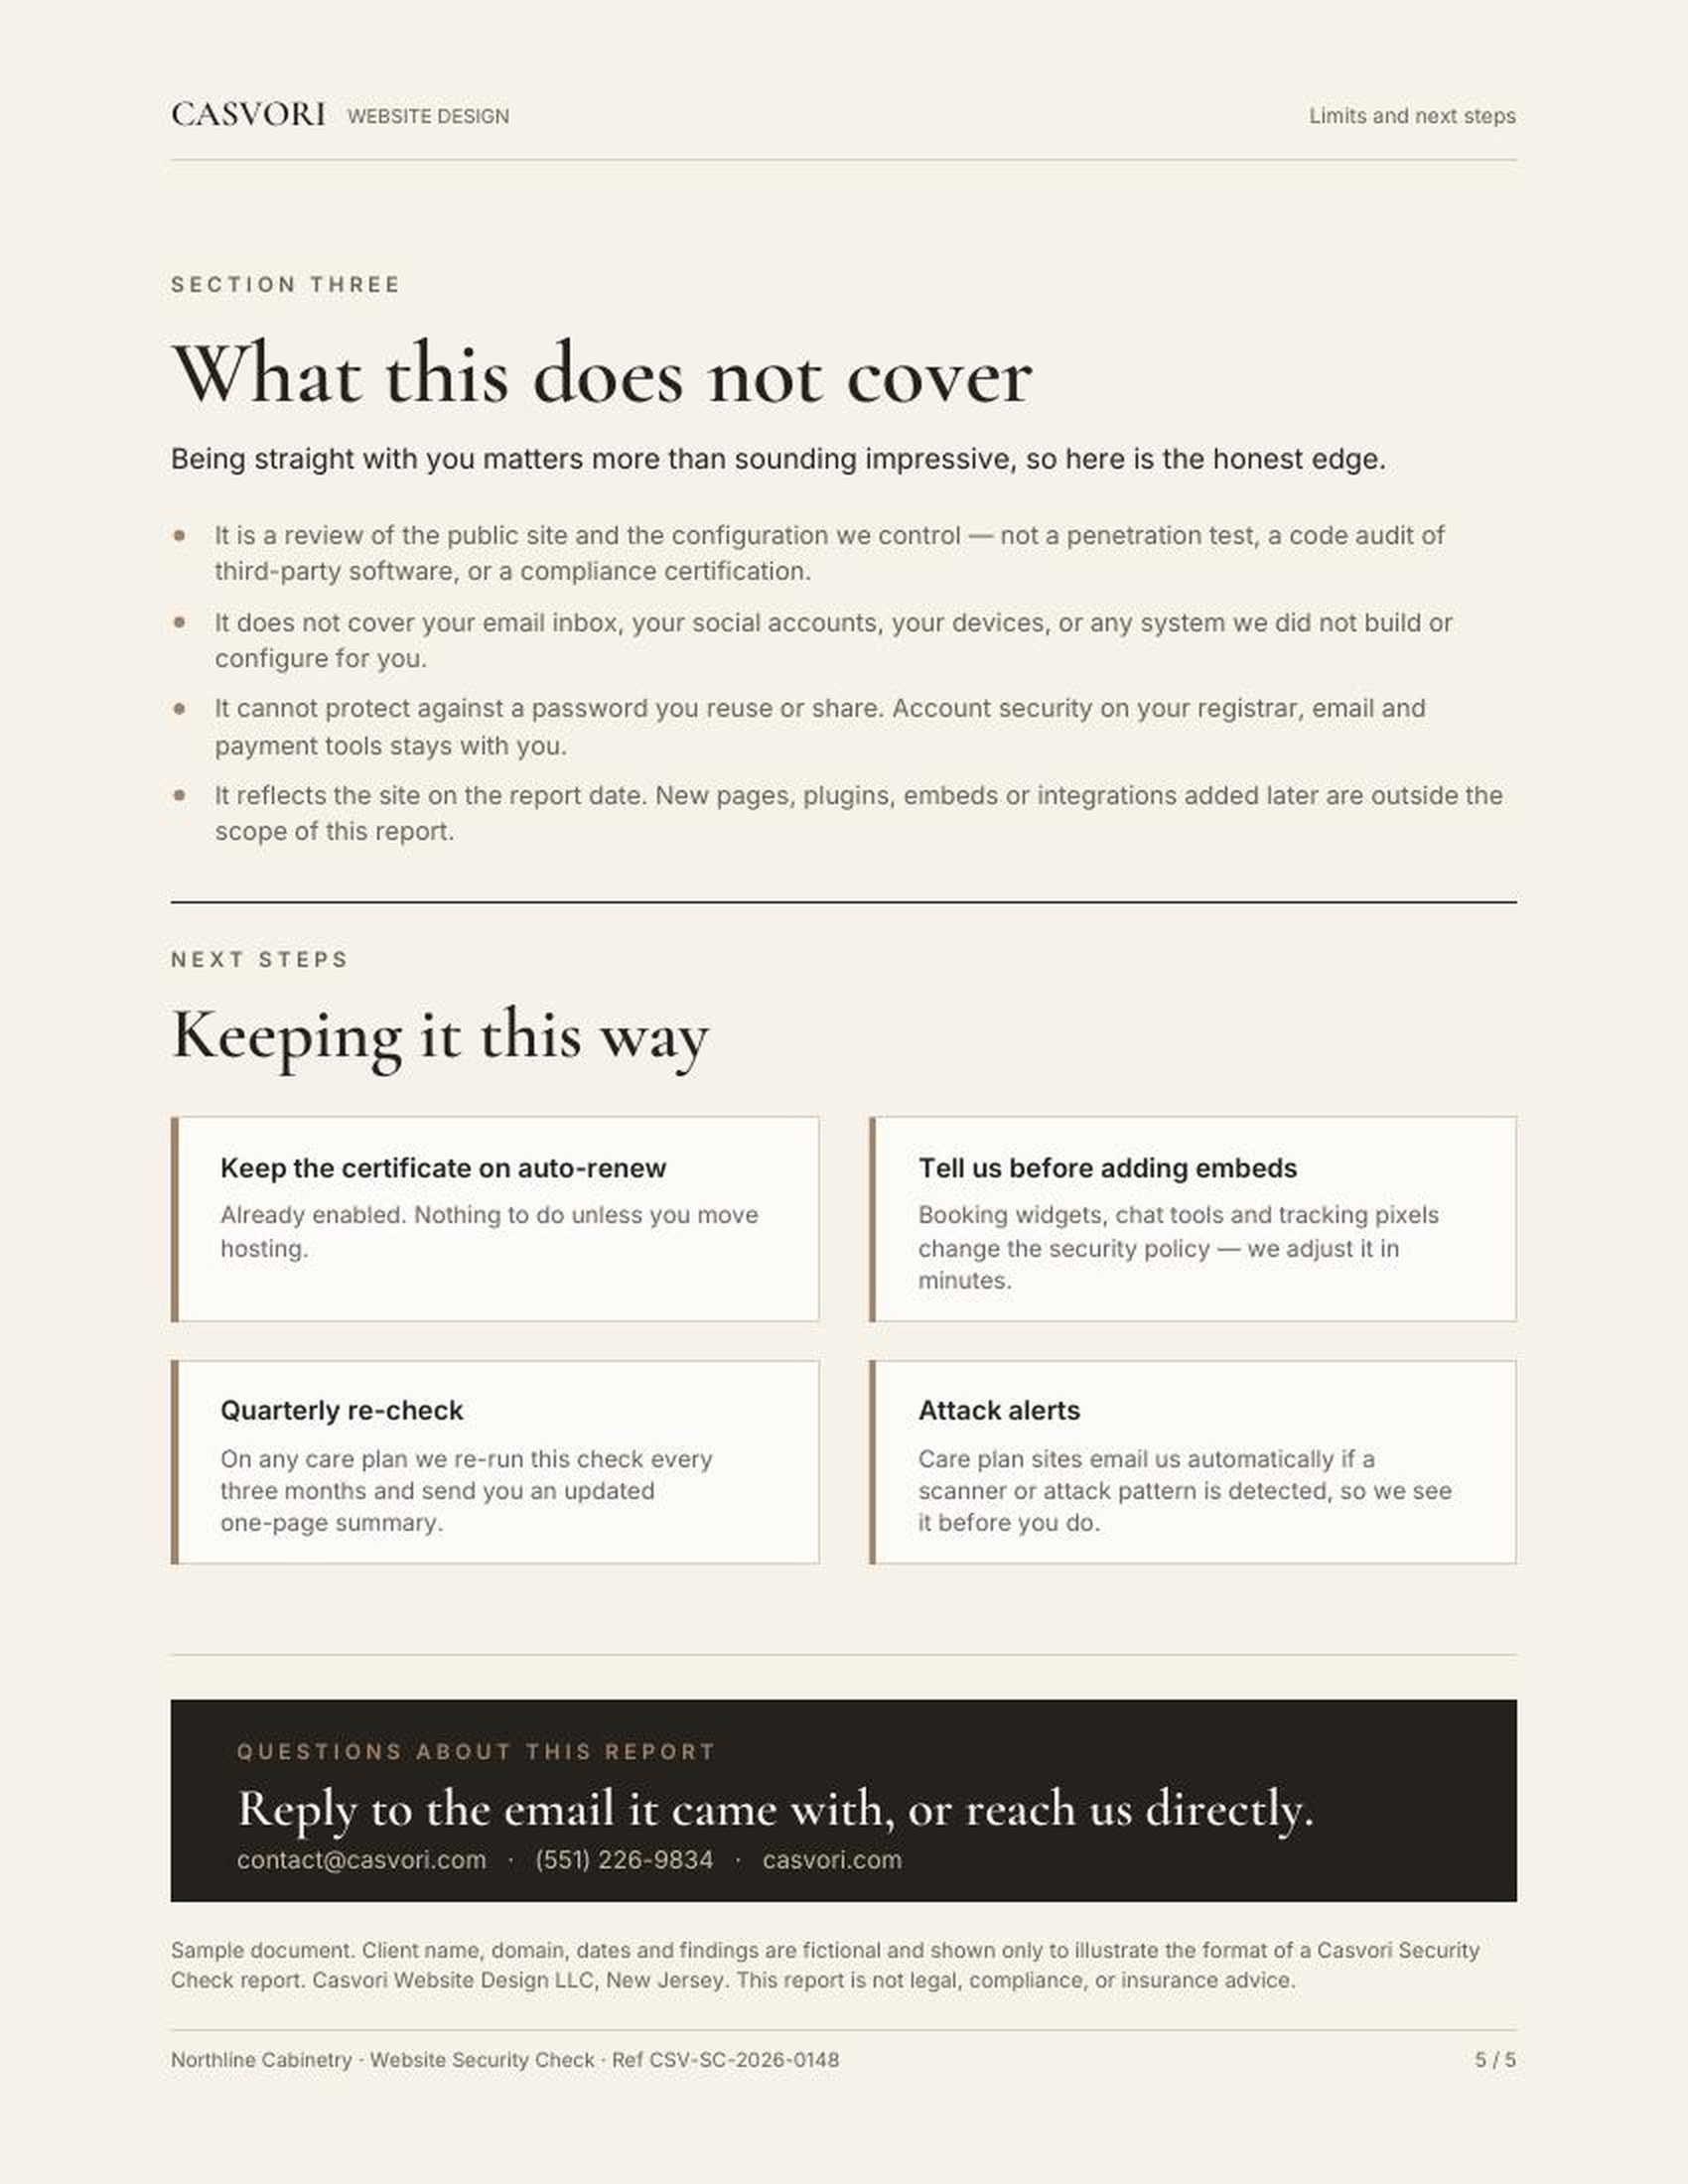
Open the full sample PDF. Client name, domain and findings are fictional — the format, the tone and the limits are exactly what you'd get.
The hardening itself is standard on every site we build — you're never charged for us doing our job properly. The $49 buys the formal review pass and the written report.
Valid certificate, auto-renewal confirmed, and every plain HTTP request redirected before any content is served.
HSTS, Content Security Policy, clickjacking, referrer and MIME-type headers reviewed and tightened to what your site actually uses.
Spam, profanity and payload-size filtering on every form, plus per-source rate limiting, verified with live test traffic.
Source maps, backups, config files and directory listings checked — anything reachable that shouldn't be gets closed.
Every package the site depends on checked against known advisories at build time, and updated where it matters.
SPF and DMARC records reviewed so it's harder for anyone to send email pretending to be your domain, plus registrar transfer lock.
The check runs before launch as part of the project. Nothing to arrange — it's our own infrastructure and our own build.
We need written authorisation from the owner before we scan anything. The redesign quote form asks you to confirm it, and we keep that confirmation on file.
We don't run unsolicited scans against anyone's website, and we won't accept a request to test a site you don't own or control.
The honest edges matter more here than anywhere else on the site.
No. It's a configuration review of the public site and the settings we control, run with industry-standard scanning tools and by hand. We don't guess passwords, exploit anything, or touch customer data. If you need a formal penetration test or a compliance audit, that's a specialist security firm's job, and we'll say so.
For a site we build, it's part of the work and we run it before launch. For a redesign or an existing site we didn't build, yes — we need written authorisation from the site owner before we scan anything. That's why the redesign quote form has a permission checkbox on it.
$49 as an optional pre-launch add-on with Essential, and included free with Signature and Premium. On any care plan we re-run the check every three months and send you an updated one-page summary at no extra charge.
No, and nobody honest will tell you otherwise. It reduces risk by closing the common, avoidable openings and gives you a written record of what was checked. It reflects the site as configured on the report date — new pages, plugins or embeds added later are outside its scope.
On a care plan, scanner activity and attack patterns email us automatically, so we usually see it before you do. Off a care plan, email us and we'll look — the fix is quoted like any other work.
A Security Check is a point-in-time review, not a certification, compliance audit, or penetration test, and no website can be guaranteed secure. Full details are in our Terms. Questions? Email contact@casvori.com.
Not building with us?
A standalone Security Check for any website you own or are authorised to approve: paid up front, permission confirmed in writing, and a plain-English report with a prioritised fix list — $49 for one site.
Security test my siteQuestions first? contact@casvori.com
Full details in our Terms and Privacy Policy.