
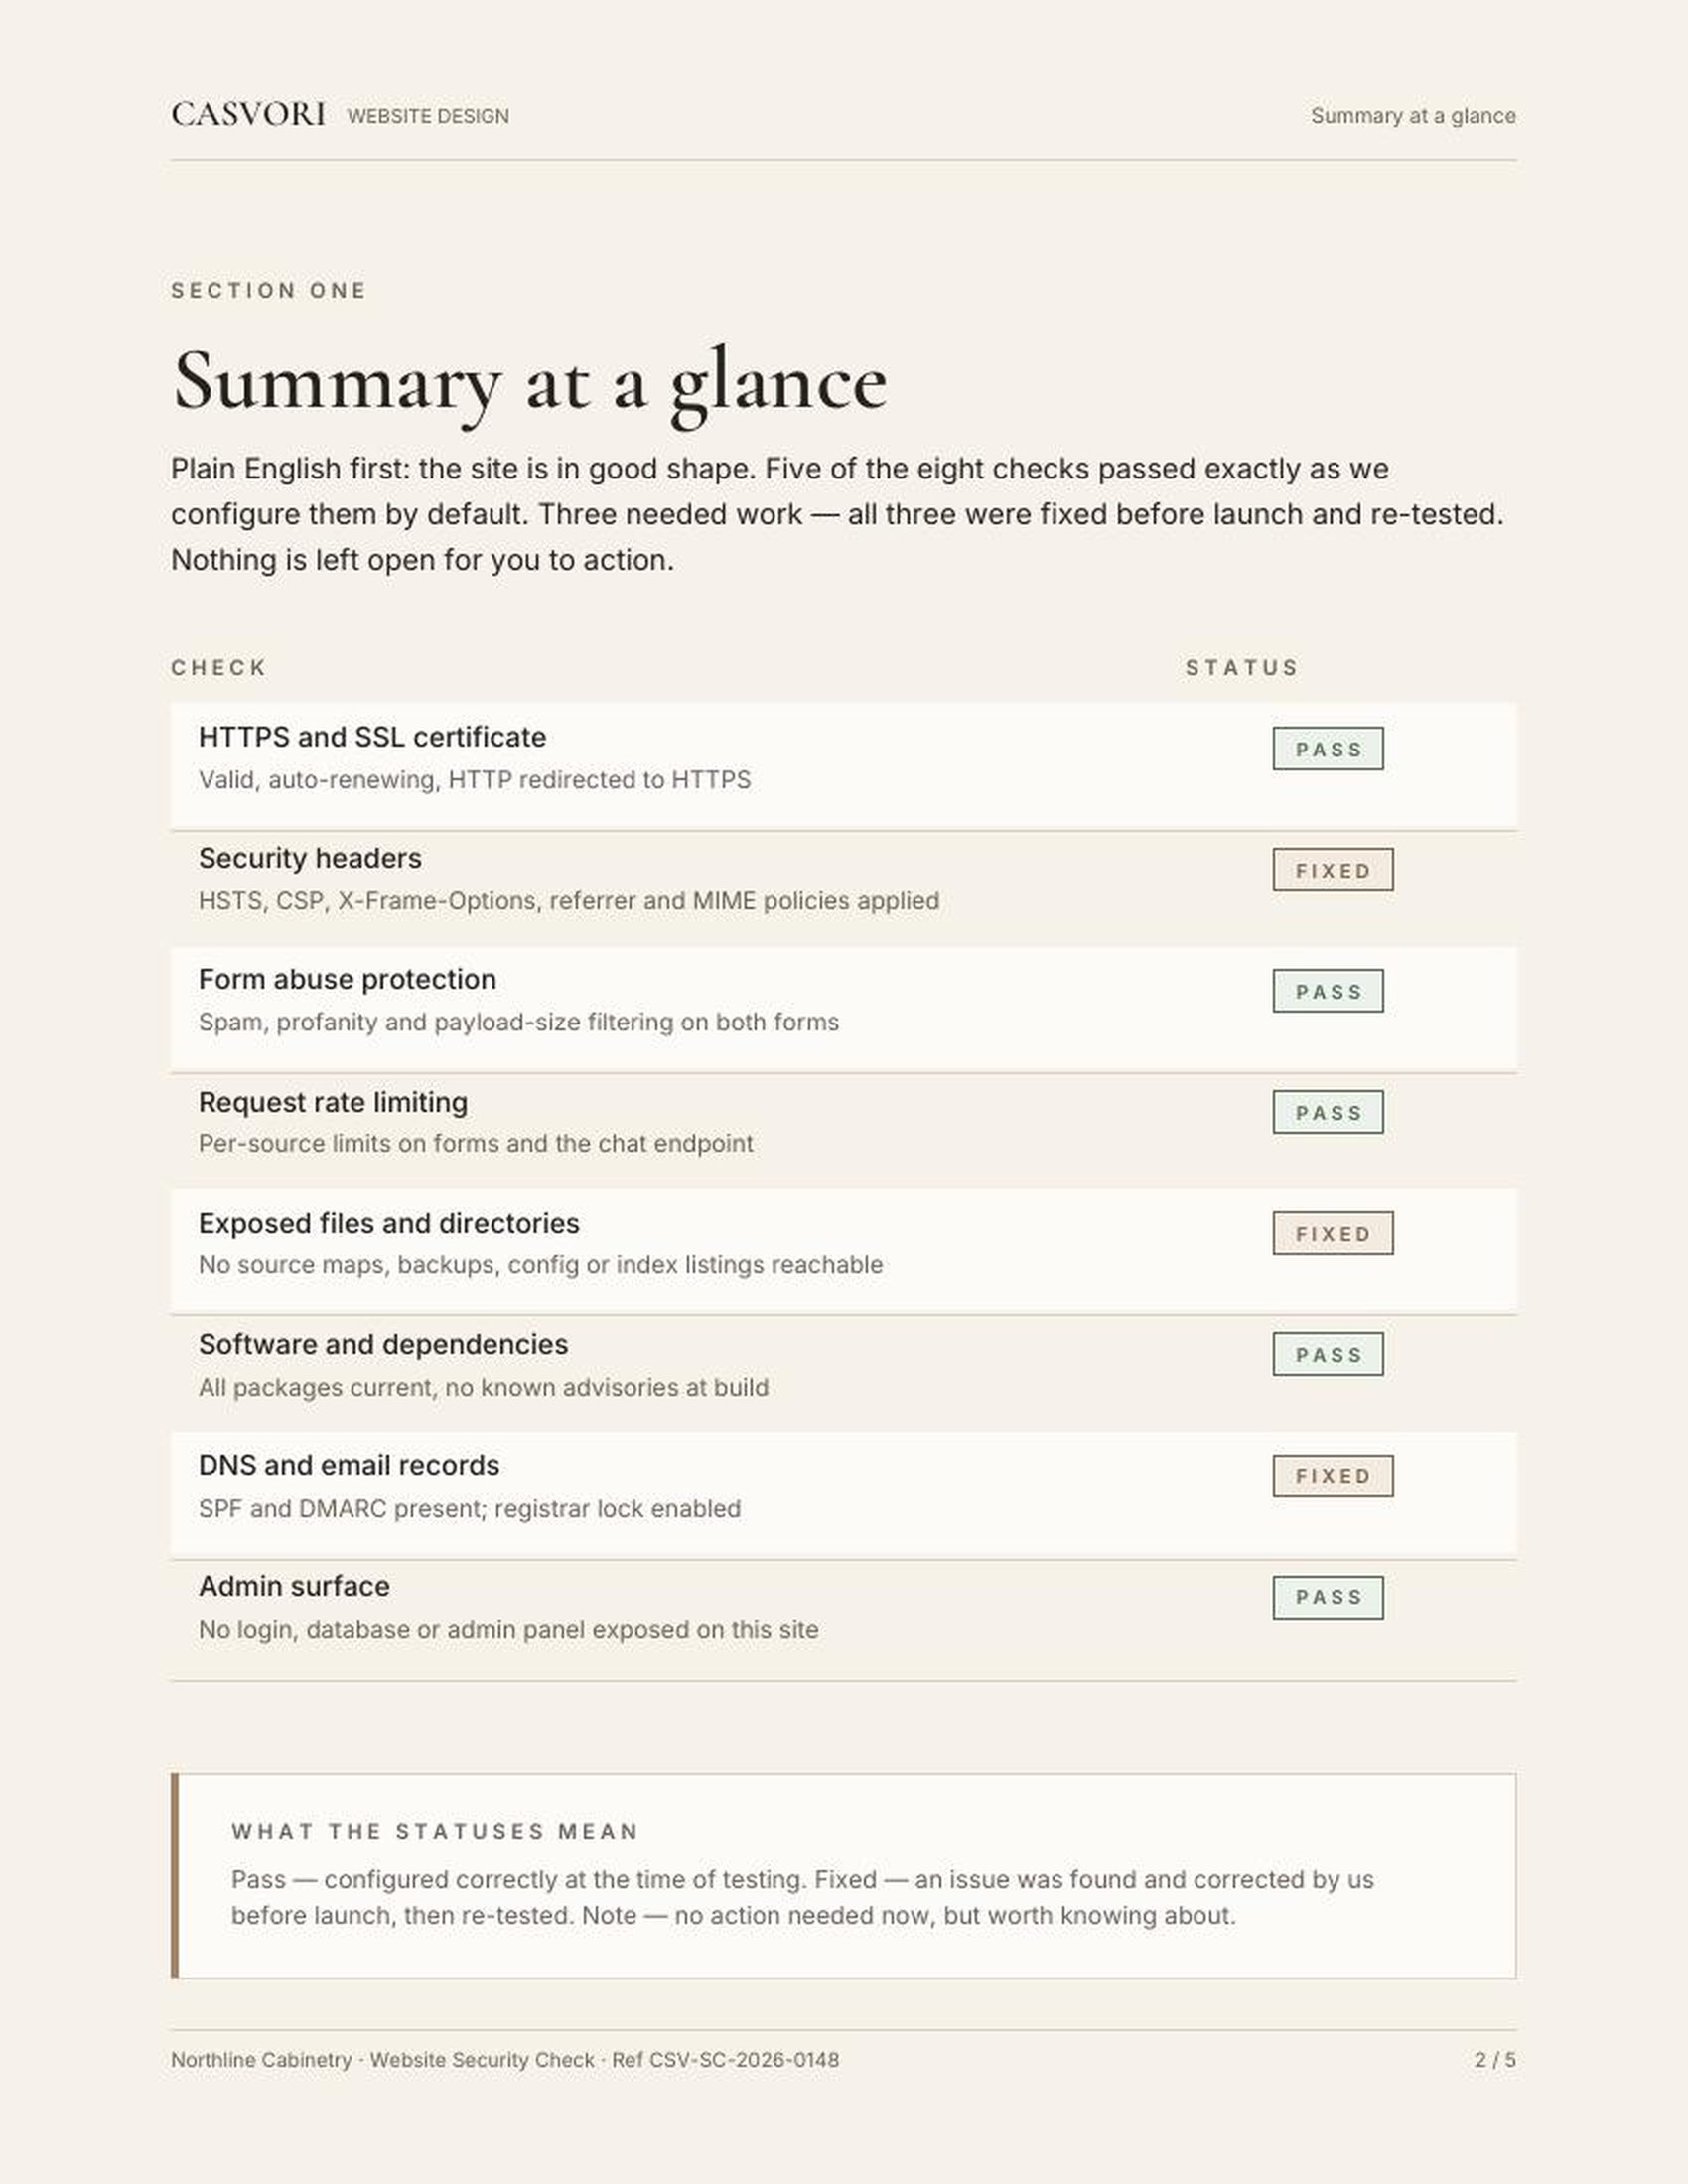
HTTPS and certificate
Valid certificate, renewal in place, and every plain HTTP request redirected before content is served.
You don't have to buy a website from us. Send us a site you own, we agree a quiet testing window, and you get a written report in plain English: what we found, what it means, and what to fix first.
Automated security scanning across the whole public site, then a manual review of every alert so you get findings, not noise.
Valid certificate, renewal in place, and every plain HTTP request redirected before content is served.
Content Security Policy, HSTS, clickjacking, referrer and MIME-type headers checked against what your site actually needs.
Session and tracking cookies checked for the Secure, HttpOnly and SameSite flags that stop them being read or replayed.
Contact and booking forms tested for injection handling, oversized payloads, spam exposure and missing rate limiting.
Backups, config files, source maps, directory listings, server version banners and debug output — anything reachable that shouldn't be.
The platform, theme and plugin versions in use checked against publicly known advisories.
SPF and DMARC reviewed so it's harder for anyone to send email pretending to be your domain.
Automated tools over-report. We work through every alert by hand and tell you which ones are noise, and why.
Worth reading before you agree to anything — from us or anyone else.
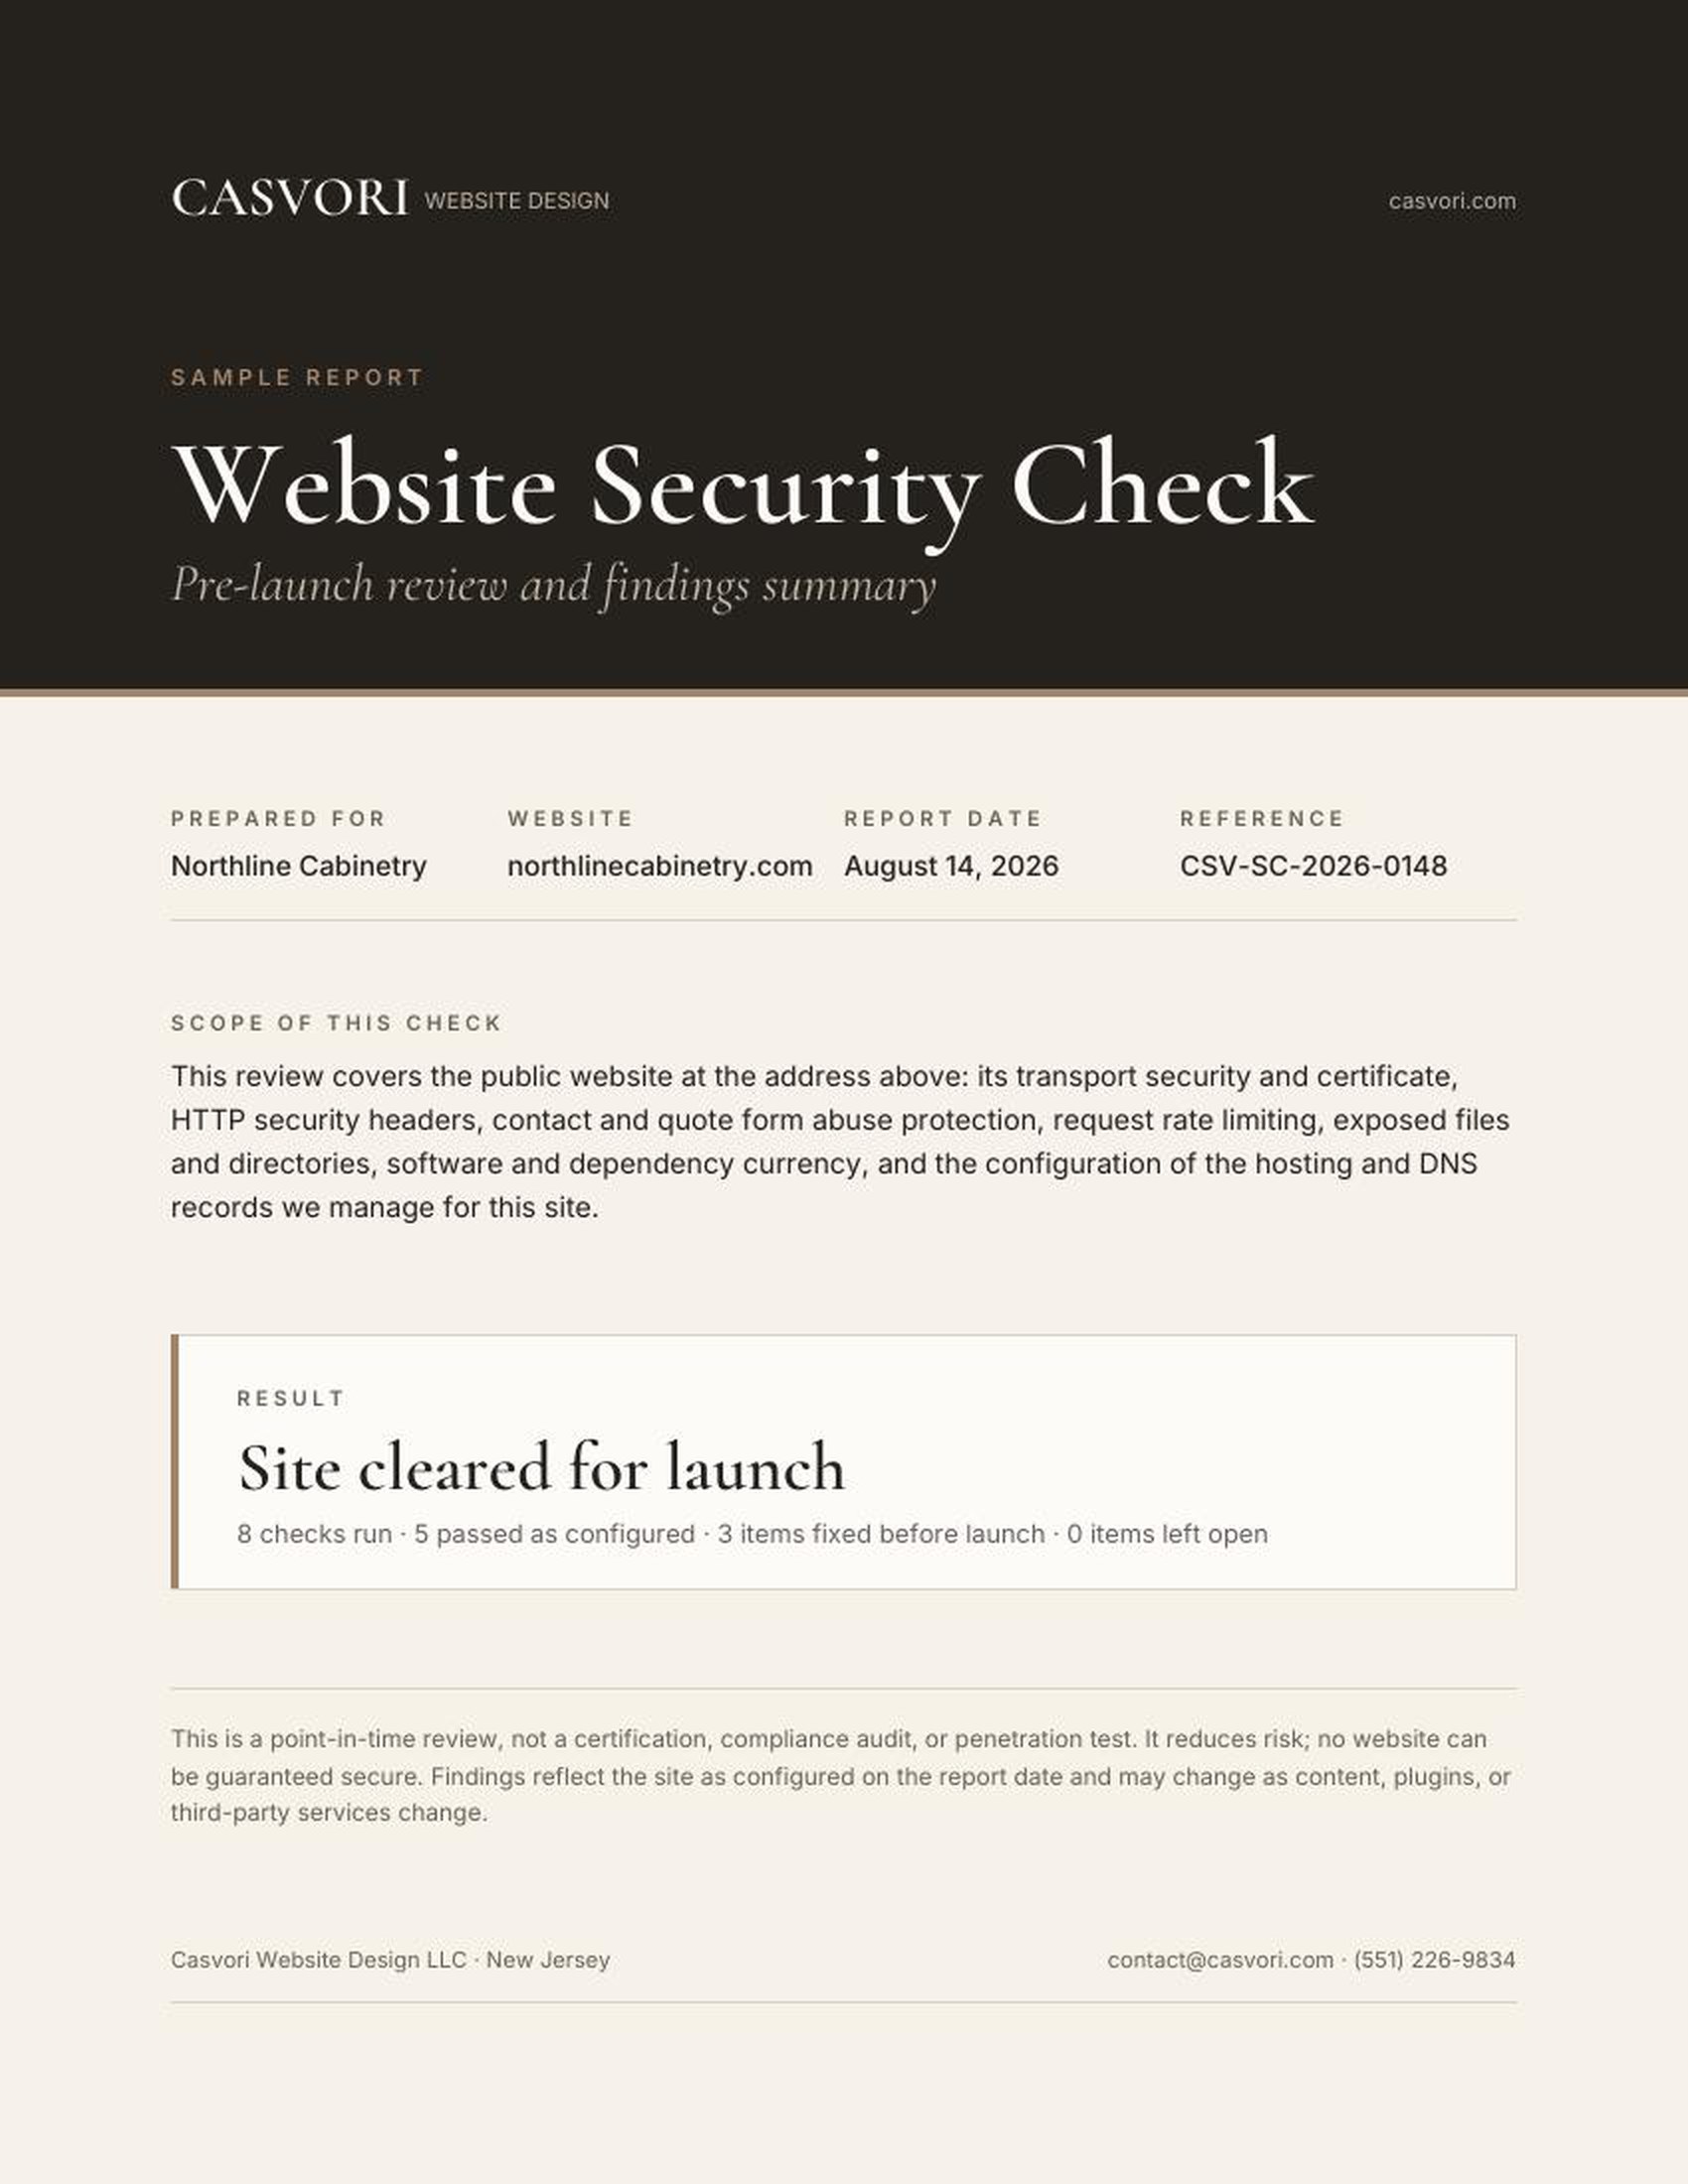
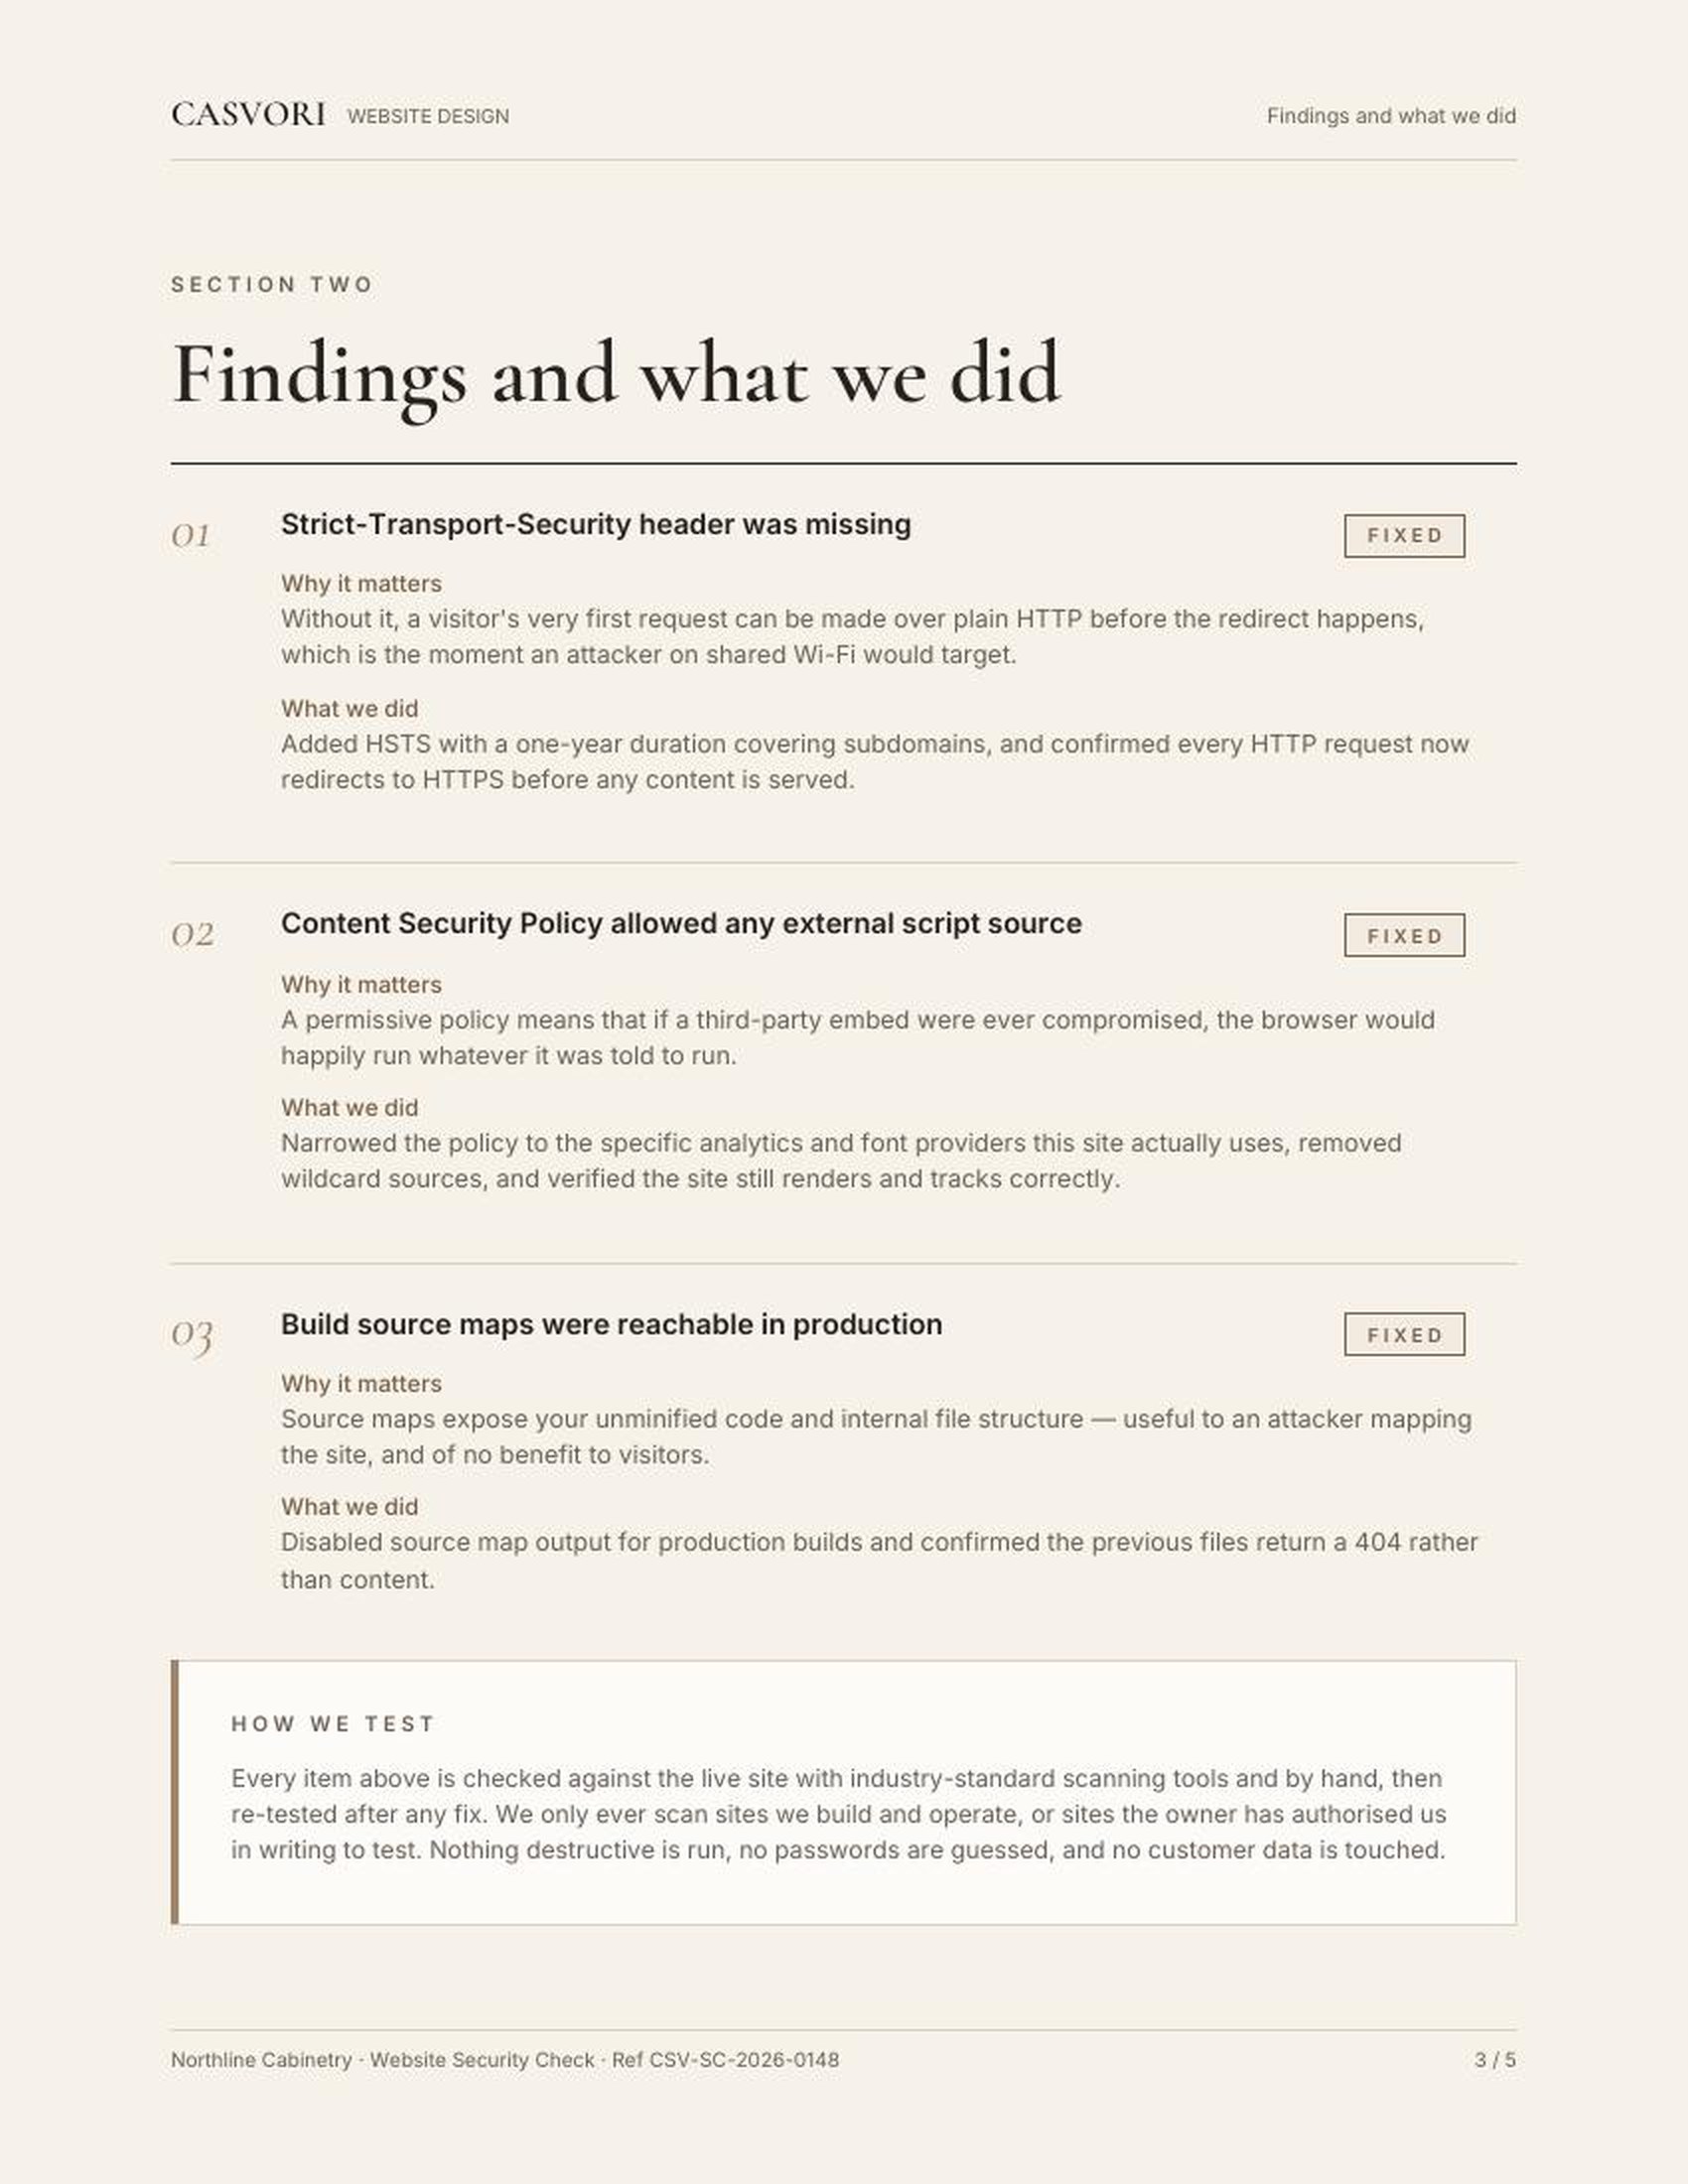
A real example written for a fictional client. Same structure, same tone, same limits.
Including the reasons you might not need us at all.
No. This is a standalone service for a site you already have, wherever it was built and whoever hosts it. If you'd rather we rebuild the site too, that's a separate quote and the check is cheaper as part of it.
The tools are free the way a table saw is free to someone who doesn't own one. The work is configuring the scan, reading a raw report that flags forty things of which six matter, and writing it up so a business owner can act on it. If you'd genuinely rather run it yourself, you should — we'd tell you the same over email.
No. It's automated security scanning plus a manual configuration review of your public site. We don't exploit anything, guess credentials, or touch customer data. A formal penetration test is a specialist security firm's job and we'll say so if that's what you need.
It's very unlikely, but not impossible — active testing sends real requests, and a fragile or heavily loaded site can slow down while it runs. That's why we agree a quiet window with you first, why we ask you to flag any forms that email real customers, and why we stop immediately if anything looks wrong.
We stop and email you the same day rather than waiting for the report. Fixes on a site we don't host are quoted separately — the $49 covers the scan, the written report, and a prioritised fix list you can hand to whoever maintains the site.
Up front, by card, at the end of the request form — $49 for one site. If we build your website on the Signature or Premium plan, the check is included free and you don't pay for it separately. Payment is what books the work; we then reply within one business day to confirm scope and agree a testing window, and nothing is tested before you say go. If we decide we can't take the job, or you can't give the permission we need, we refund you in full.
Yes, always, and the form asks for it in writing. Testing a website you don't own or aren't authorised to approve is not something we'll do, no matter who asks. Some hosts and platforms also require their own approval — that part is yours to arrange.
A Security Check is a point-in-time review, not a certification, compliance audit, or penetration test, and no website can be guaranteed secure. It reflects the site as configured on the report date. Full details are in our Terms. Questions? Email contact@casvori.com.
Full details in our Terms and Privacy Policy.